Heavy Wizardry 101
Price:
Sale price
£39.90
Stock:
Coming Soon
Login / Signup
Cart
Your cart is empty




Forget waving wands - the real magic happens in assembly. Heavy Wizardry 101 takes you deep into shellcode, backdoors, worms and low-level hacking across x86_64, ARM, MIPS and RISC-V.
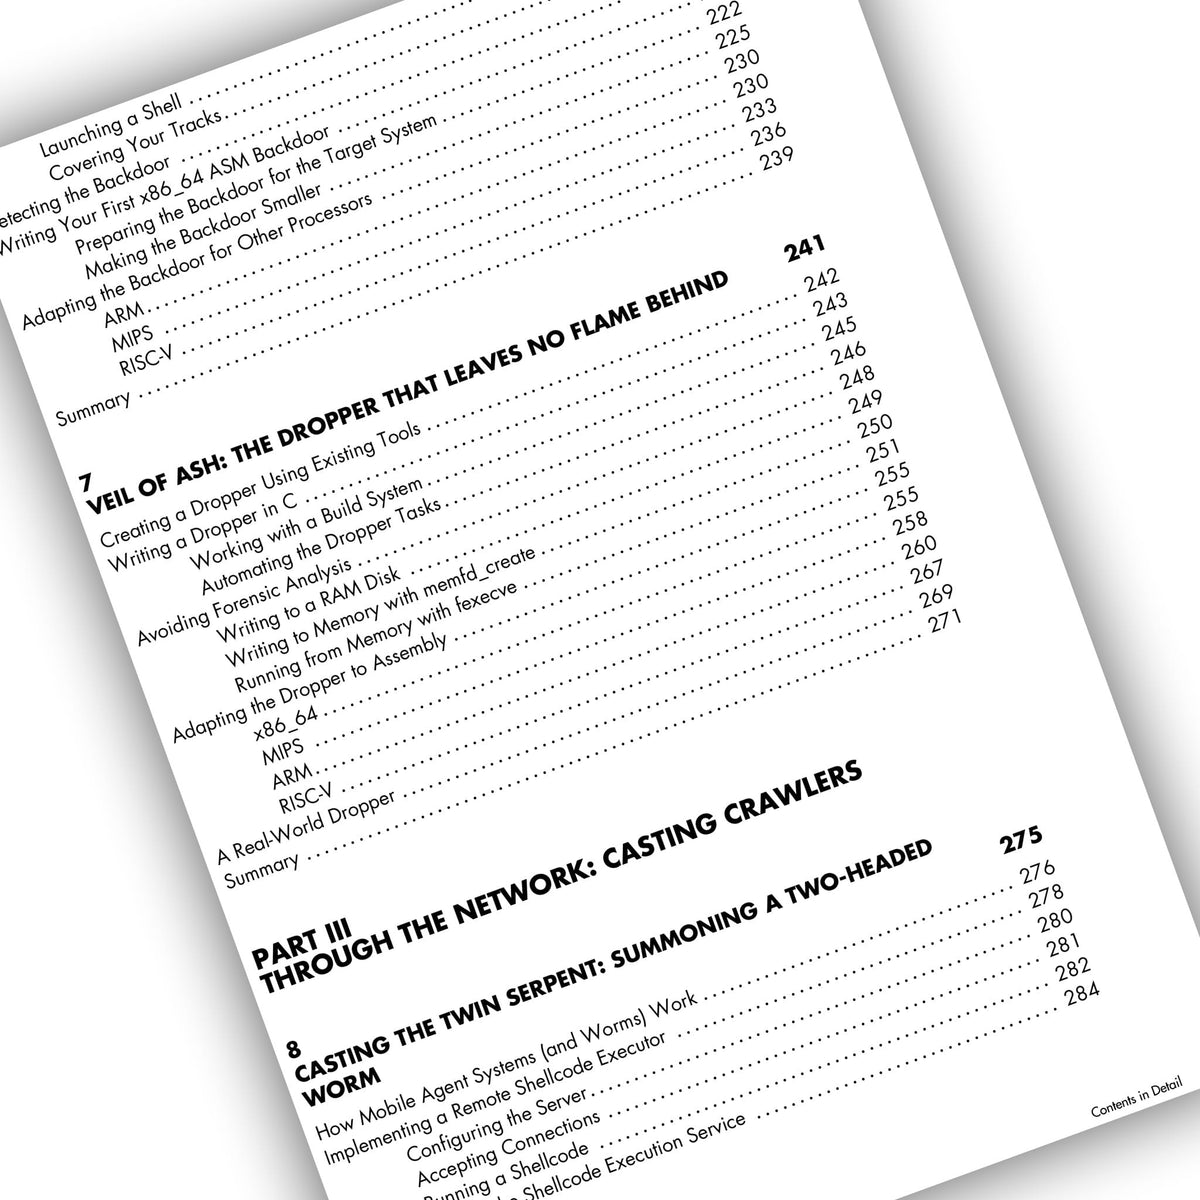
In hacker circles, 'heavy wizardry' means code that trades on intimate knowledge of a system - the kind that speaks its private dialects and bends its rules. Heavy Wizardry 101 teaches you to write it. You’ll build shellcode, backdoors, droppers, and worms from scratch, working at the instruction level where magic happens.
Every project is implemented for four architectures: x86_64, ARM, MIPS, and RISC-V. You’ll write the same program four times, seeing exactly what stays constant and what changes. Each chapter starts with architecture fundamentals, such as memory layout, calling conventions, and stack mechanics, then walks through complete working implementations on Linux in safe, contained environments.
Learn to:
Whether you’re a penetration tester who wants to stop depending on Metasploit, a security researcher analysing malware, or a systems programmer who needs to understand how computers work, this book gives you the skills to build and reason about code at the lowest level.
David Martínez Oliveira, aka Pico, has been writing code close to the metal since the 1990s, building software for computer vision, communications systems, laboratory equipment, and AR/VR/MR applications. A longtime GNU/Linux user, he explores security and low-level system internals both professionally and for fun.
Your payment information is processed securely. We do not store credit card details nor have access to your credit card information.